
Cloudflare has detected millions of attempts to exploit two critical vulnerabilities in PHP since details of the flaws were disclosed on Wednesday, according to the company’s Chief Executive Officer, Matthew Prince.
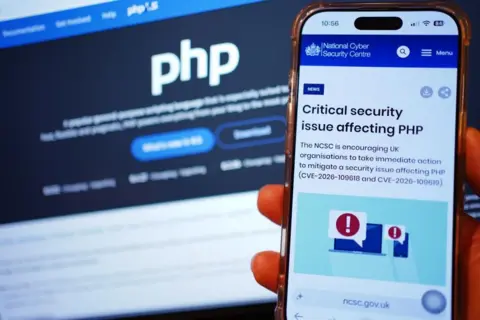
The vulnerabilities affect PHP, a programming language widely used to build and power websites across the internet.
Prince disclosed the figures in a post on X, saying Cloudflare had detected thousands of exploitation attempts in the 10 hours before the vulnerabilities became public.
The number surged to tens of thousands within 45 minutes of the disclosure, reached hundreds of thousands within two hours and climbed into the millions by the time of his post.
Dubbed PHP2Shell, the vulnerabilities allow attackers to execute code on web servers without logging in.
PHP rated both flaws 9.2 out of 10 for severity and released emergency security patches for versions 8.2 through 8.5 on Wednesday, a day earlier than planned, after technical details of the vulnerabilities leaked online.
PHP has urged users to install the security updates immediately to protect their systems from potential attacks.
Cloudflare activated firewall rules for all customers, including those on free plans, about nine hours before the vulnerabilities were publicly disclosed.
However, the company warned that the rules provide only temporary protection and stressed that users must still update their PHP installations to address the flaws.