
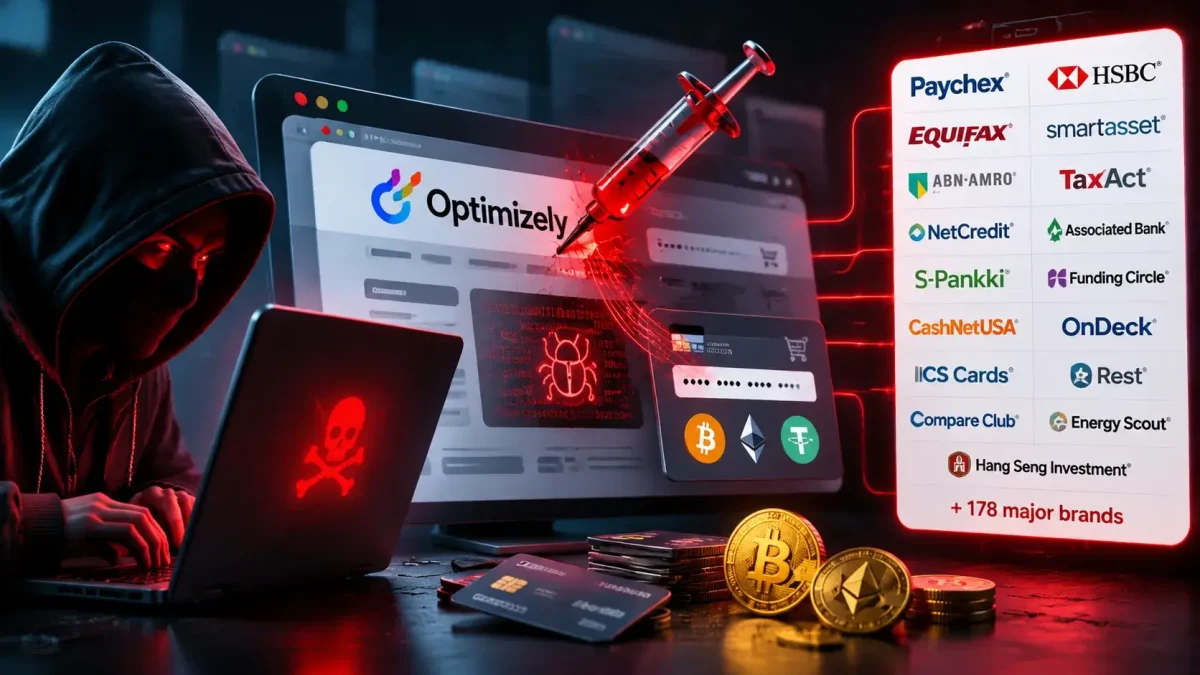
Hackers exploited Optimizely, a website testing platform, to distribute malware to visitors of at least 178 organisations on Monday, affecting websites operated by Zoom, the BBC, CNN, Fox News, Salesforce, GitLab, IKEA, HSBC and Equifax.
Optimizely confirmed the breach, telling BleepingComputer that an unauthorised party had exploited a vulnerability in the signup process for its Experimentation account.
“They used it to add malicious JavaScript to some customer projects. We have blocked access to the vulnerable path and deployed a fix,” Optimizely stated.
Optimizely said it had removed the malicious code, terminated active sessions, revoked access tokens and notified all affected customers.
However, its incident notice, published at 01:02 UTC on Tuesday, did not disclose the number of projects compromised or explain how the vulnerability was exploited.
Security researcher Scott Helme of Report URI first uncovered the attack. His team examined 1,611 Optimizely scripts and discovered malicious code in 188 of them, affecting 178 organisations. However, he warned that the actual number of affected organisations was likely higher.
Websites use small Optimizely scripts to conduct experiments on their platforms.
The attacker inserted malicious code into the custom section of customers’ projects, allowing it to be distributed through Optimizely’s servers without directly modifying the affected websites’ own code.