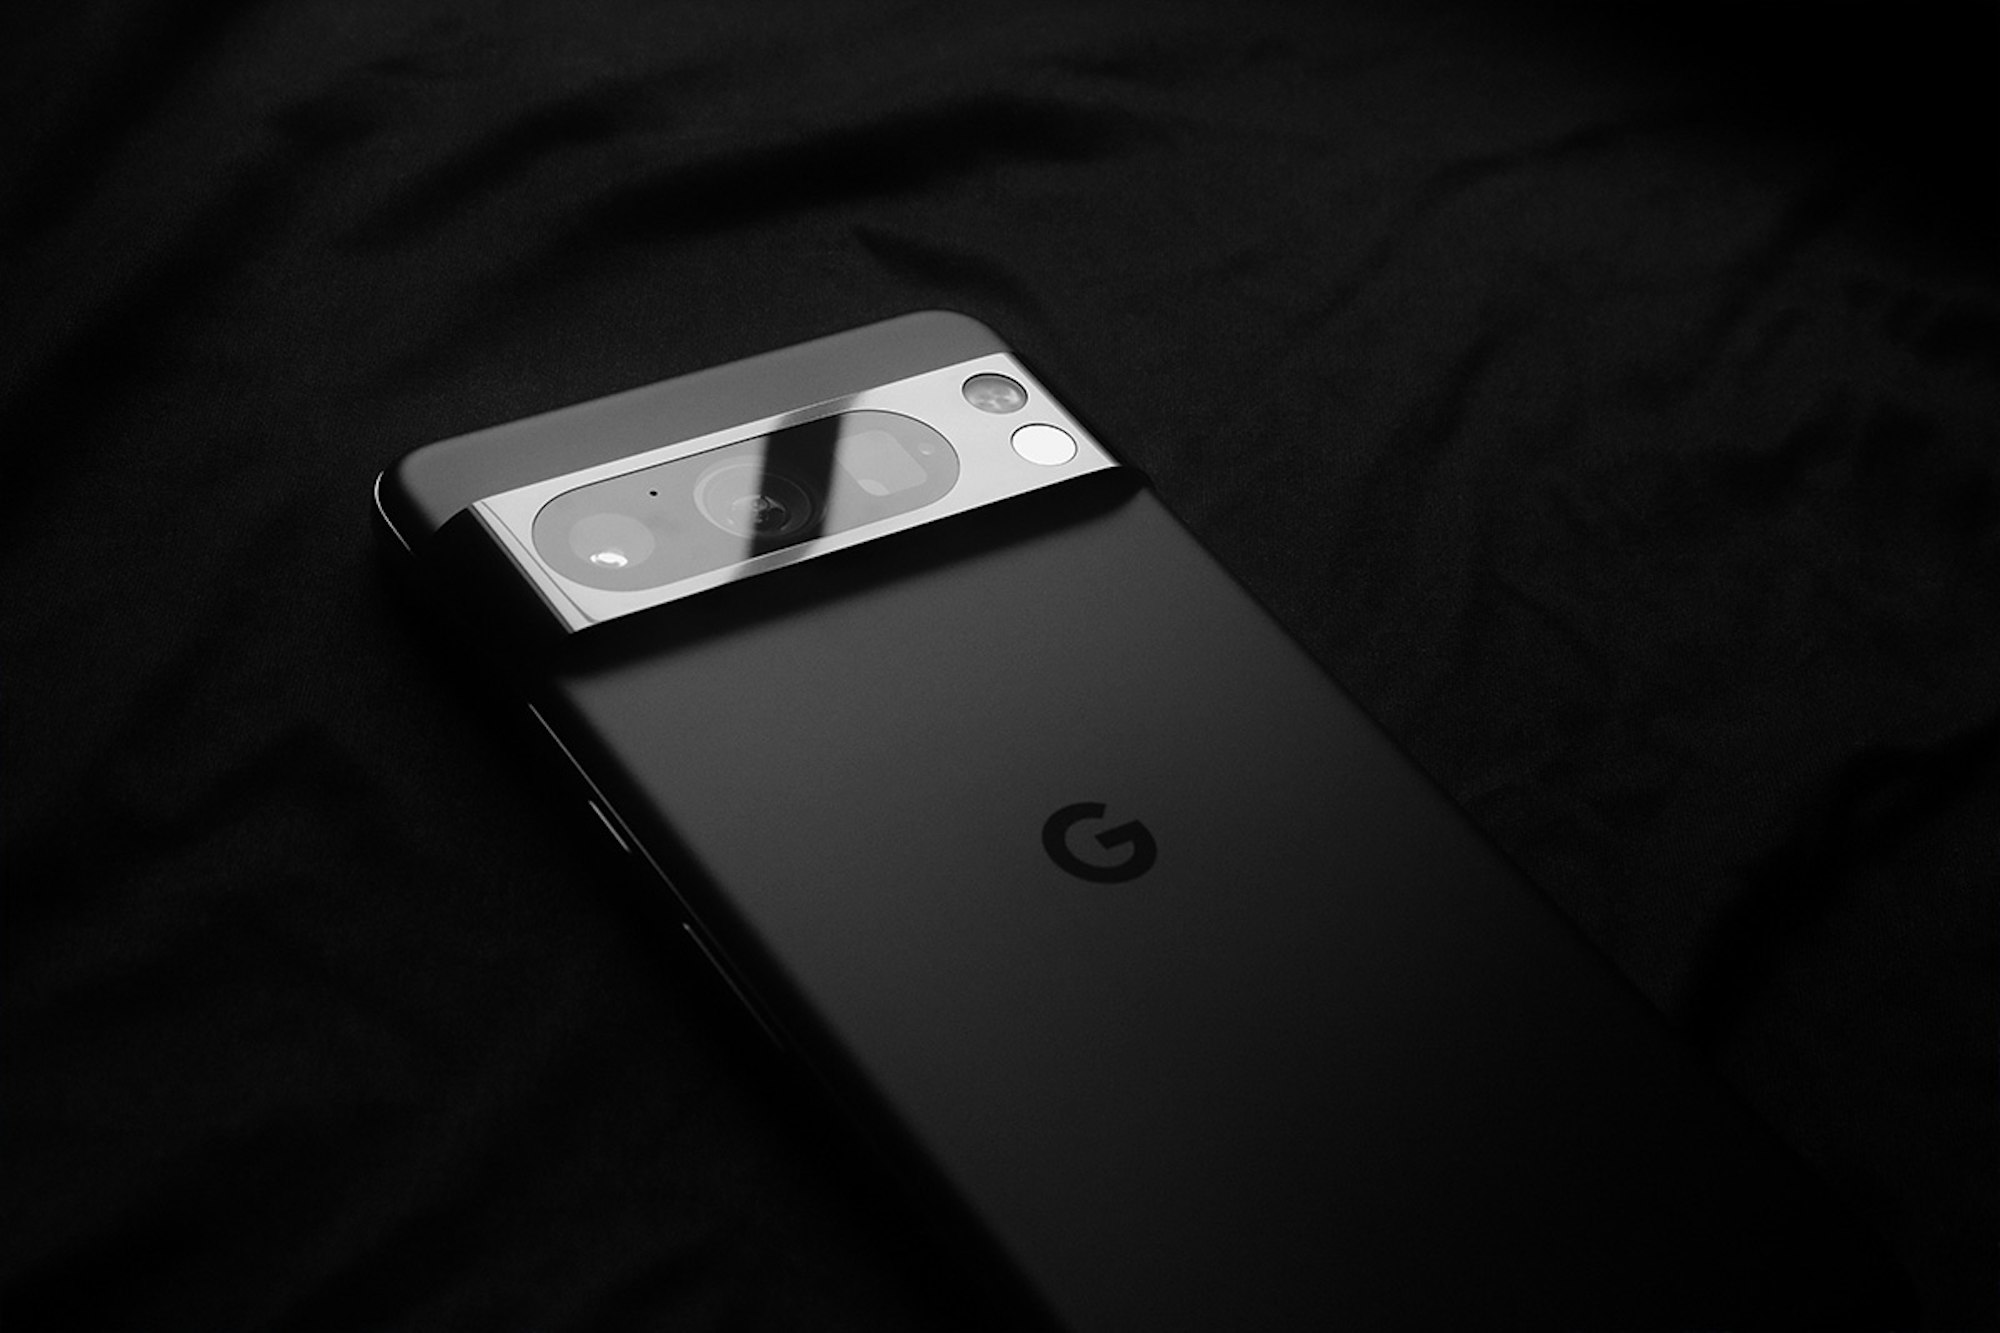
Google has disclosed that a software vulnerability in its Pixel smartphones was exploited in limited and targeted cyberattacks before the company released a patch to address the flaw.
The vulnerability, tracked as CVE-2026-58704, was disclosed by Google on Tuesday and affects the modem component of Pixel devices, which handles the phone’s connection to mobile networks and the internet.
According to Google, exploitation of the flaw could allow an attacker to break out of the modem’s security sandbox and gain access to data and functions elsewhere on the smartphone.
The vulnerability is classified as a privilege-escalation flaw.
The bug is particularly concerning because it can be exploited through a zero-click attack, allowing an attacker to compromise a device without requiring the owner to click a link, open a file or otherwise interact with the phone.
Google has provided limited technical details about the attacks and has not disclosed who was behind the exploitation.
The company said the vulnerability has now been patched, although it did not provide further details about the devices affected or how the attacks were carried out.
Such vulnerabilities can attract the attention of commercial surveillance companies that develop spyware capable of accessing data from targeted devices. These firms often sell surveillance tools to governments and law enforcement agencies.